Governments love a simple soundbite. Tell Apple and Google to switch on a magic switch, stop children from sending or viewing nude images on their smartphones, and watch the headlines roll. It sounds clean. It sounds protective. But if you look past the political posturing, you hit a massive wall of technical headaches, privacy battles, and practical realities that politicians rarely mention.
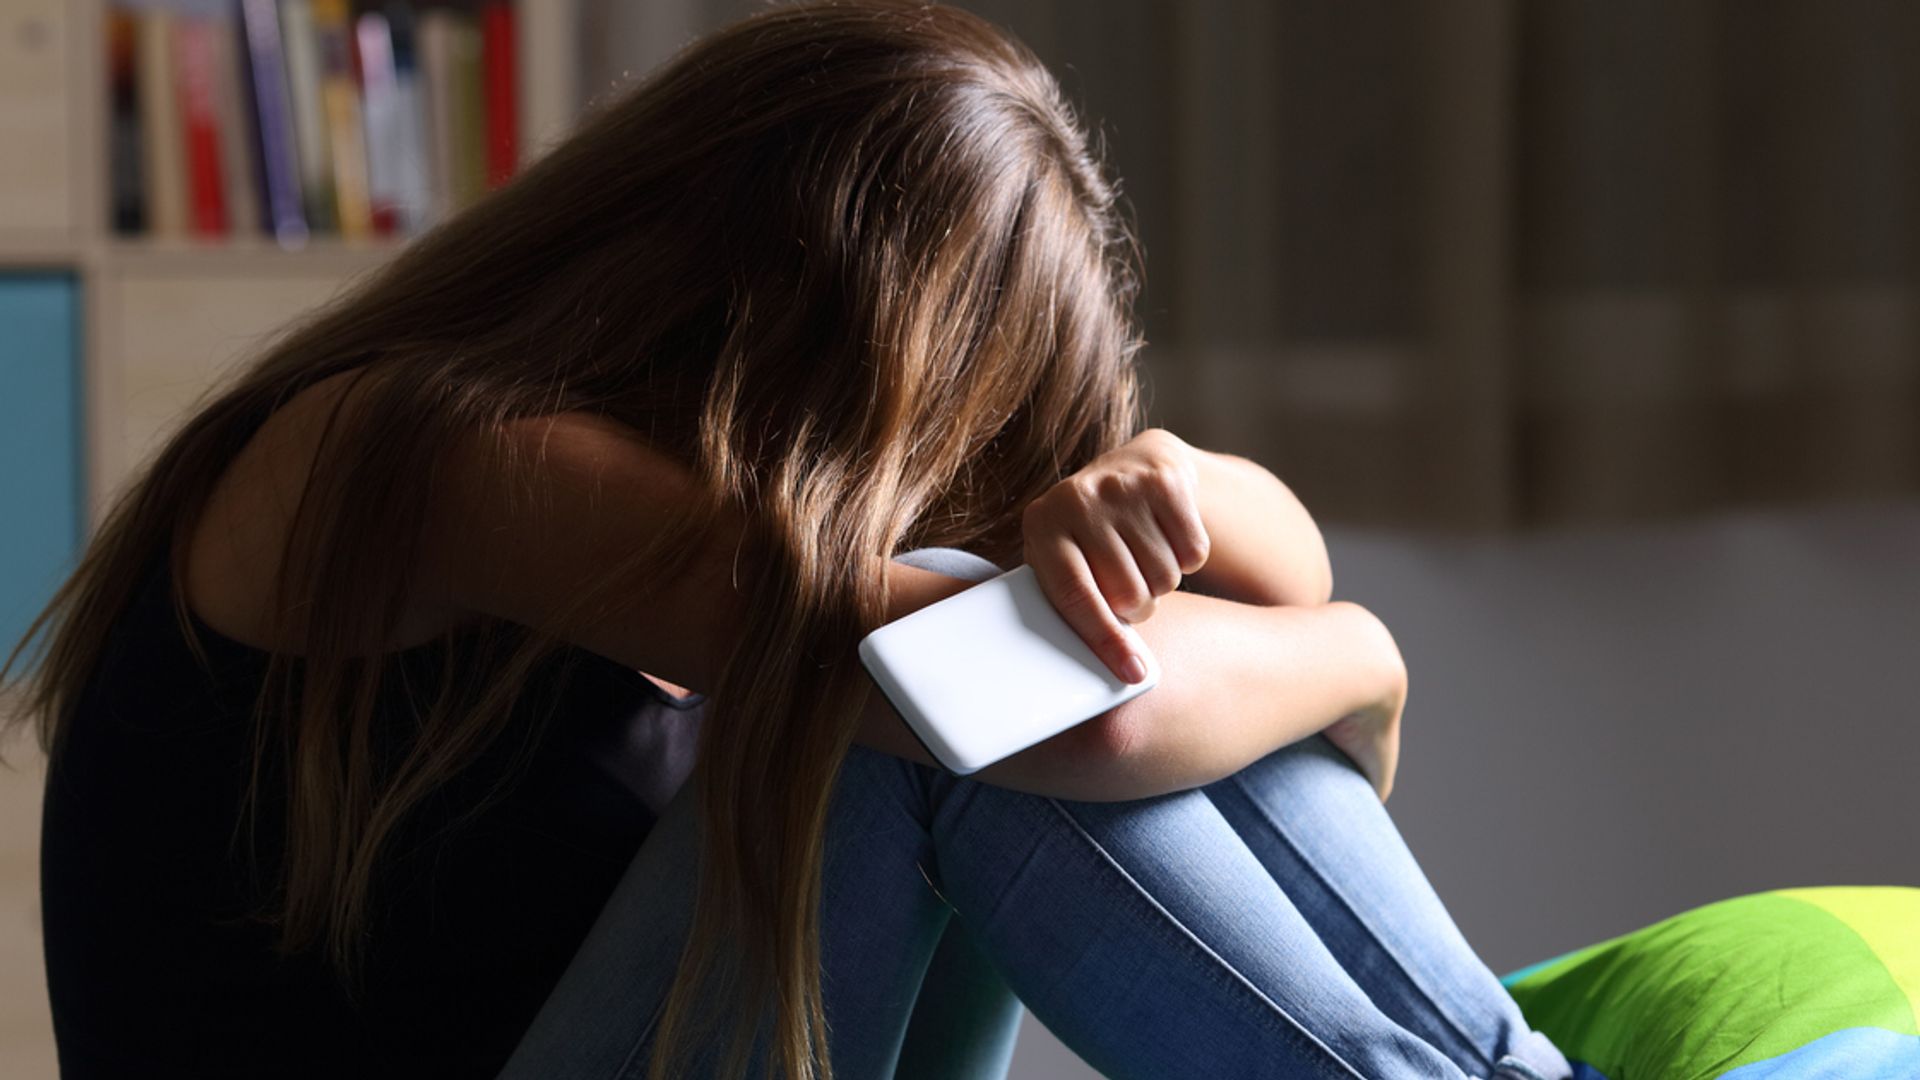
Over a hundred MPs recently cranked up the pressure, signing a direct letter warning that explicit images are increasingly weaponized to groom, exploit, and blackmail minors. Child safety organizations like the NSPCC and the Molly Rose Foundation are backing the push, arguing that tech giants have dragged their feet while young people face preventable harm.
Yet, forcing multi-trillion-dollar corporations to police device-level imagery opens up a Pandora's box of complex questions. How do you scan a device without breaking end-to-end encryption? Where is the line between child safety and mass surveillance? And what happens when the software inevitably gets it wrong?
The Core Problem No One Wants to Address
The statistics driving this political pressure are brutal. A staggering portion of online child exploitation reports center on self-generated imagery—often called sexting or youth-produced sexual material. Kids are handing over or being coerced into sharing photos they shouldn't, and the fallout can be catastrophic.
Platforms argue they already employ communication safety tools, like Apple's features that blur explicit photos sent or received via messages. But child safety advocates want a blanket, default-on solution built right into the operating system level across all apps and devices. They want it impossible for a child to take, store, or transmit explicit content in the first place.
Here is where the friction starts. Apple and Google operate in global markets with vastly different regulatory frameworks. Building a bespoke UK-only or regional constraint into core device architectures creates massive engineering and compliance hurdles.
Why Client-Side Scanning Terrifies Privacy Experts
To block explicit images before they are shared or saved, a phone basically needs to inspect what is happening on the device itself. Cybersecurity researchers call this client-side scanning.
It sounds harmless until you think about how it works under the hood. For a smartphone to know an image contains nudity, an algorithm has to analyze pixels locally before encryption locks it down. Privacy advocates, including various digital rights groups, argue that building this scanning capability into every phone creates an infrastructure primed for scope creep.
Once an operating system has built-in mechanisms to scan your personal photo library or messages for specific categories of content, modifying those filters later becomes dangerously easy. Today it is explicit images. Tomorrow, authoritarian regimes or changing domestic administrations could mandate scanning for political dissent, copyrighted material, or unsanctioned speech.
That is why technical experts like Lukasz Olejnik have noted that while client-side scanning is often framed as the least dangerous compromise, it fundamentally alters the private nature of personal computing.
The Reality of False Positives and Hand-Me-Down Phones
AI and machine learning tools are notoriously bad at context. Anyone who has dealt with automated content moderation knows that algorithms struggle to differentiate between malicious exploitation, artistic expression, medical documentation, or mundane family photos.
Imagine a teenager taking a photo of a rash for a doctor, or a younger child captured in the bath by a parent on an old smartphone. If device-level nudity blockers are overly aggressive, families will face constant false positives, locked accounts, and frustrating administrative loops just to prove they aren't criminals.
Compounding this is the hand-me-down phone problem. Millions of children use older iPhones or Android devices passed down by parents. How do you retrofit deep system-level software updates onto hardware that manufacturers stopped supporting years ago? If the mandate only applies to brand-new hardware purchases, millions of vulnerable kids using older models slip straight through the safety net.
What Needs to Happen Next
Tech companies cannot simply shrug and ignore the crisis. Public pressure is mounting, and legislative momentum is real. Companies like Apple are expanding communication safety warnings, and Google continues tweaking its SafetyCore frameworks to detect sensitive content inside messaging ecosystems.
If these companies want to avoid heavy-handed, clumsy legislation, they need to invest heavily in privacy-preserving local AI models that minimize false positives while giving parents actual control. At the same time, society has to accept that software alone won't fix a cultural issue. Digital literacy, open conversations at home, and holding actual bad actors accountable matter just as much as lines of code.
Stop treating technology as a substitute for parenting and education. Fix the root causes, demand transparency from developers, and stop pretending a simple toggle switch solves a deeply human crisis.