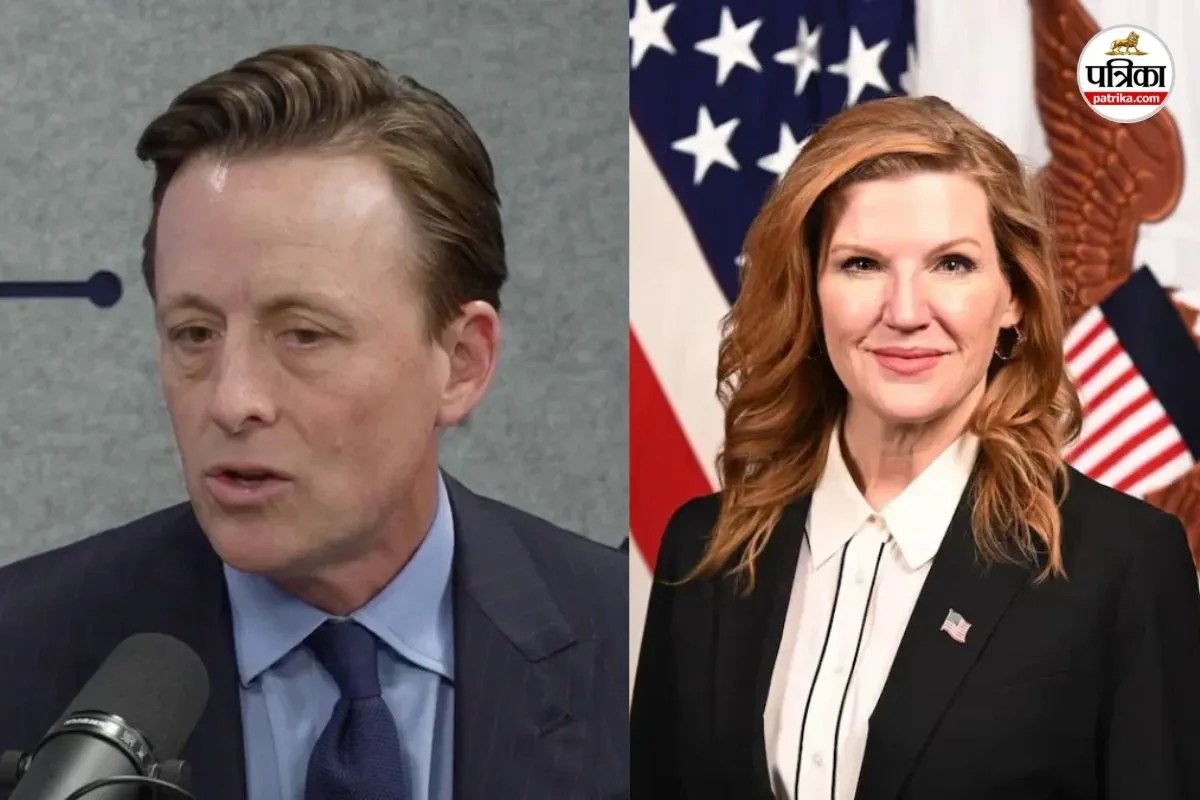
Is the United States facing a full-blown cybersecurity crisis, or did a bad string of tech hiccups simply collide with political friction inside the White House? That question got louder on November 19, 2026, when President Donald Trump moved to replace National Cyber Director Sean Cairncross and tap Pentagon Chief Information Officer Kirsten A. Davies as acting head of the Office of the National Cyber Director.
If you only read quick headlines, it looks like a dramatic wartime firing in the middle of a cyber meltdown. Look closer, though, and the story splits into two distinct tracks: real operational pain across critical systems and a fierce internal debate over whether those disruptions were cyberattacks, routine failures, or symptoms of deeper fragility.
In my years working around enterprise resilience and security operations, one rule always holds true. When outages stack up across aviation, banking, and communications within days of each other, people immediately suspect an adversary. Sometimes they're right. Often, brittle shared infrastructure and rushed updates are the real culprits.
Why Sean Cairncross Lost His Post After Fifteen Months
Sean Cairncross had been leading federal cyber policy since his Senate confirmation in August 2025, bringing a political and operational background from his time as chief operating officer of the Republican National Committee and a senior adviser during Trump's first term. On paper, he had executive and political muscle. In practice, critics inside and outside Washington questioned whether he had deep technical cybersecurity credentials for a role that coordinates policy across agencies, private infrastructure operators, and intelligence bodies.
Reporting from outlets including CBC News and HDI / HSToday indicates that Trump backed removing Cairncross amid concerns over his cyber qualifications and friction around outages and artificial intelligence safety issues. Meanwhile, the White House framed the exit around stepping down, and Cairncross publicly described serving under Trump as a major honor.
That gap between "fired over credentials" and "stepping down" isn't unusual in Washington. Administrations rarely air every internal dispute publicly on day one. What matters more is the timing. Replacing the head of the Office of the National Cyber Director right after high-profile service disruptions sends a blunt signal that the White House wanted a more technically seasoned figure—at least in an acting capacity—while a permanent Senate-confirmed pick remains down the road.
Is the US Facing a Real Cybersecurity Crisis or Fragile Tech?
Here's the honest answer: there is a resilience and concentration crisis, even if officials haven't tied the recent wave of outages to a coordinated foreign cyberattack.
Over recent weeks, Americans watched several major disruptions hit daily life at once. A communications failure tied to the Federal Aviation Administration disrupted flight operations nationwide, with reporting noting massive flight impacts. Businesses and individuals also ran into a lengthy Microsoft Outlook and Teams outage, banking hiccups across major institutions like JPMorgan, Bank of America, and Wells Fargo, and internal network trouble affecting the National Security Agency.
Senior intelligence officials, the Department of Homeland Security, and President Trump have pushed back against the idea that these incidents represent a single, coordinated hostile attack. Instead, officials have pointed to separate technical snags, maintenance, and update issues rather than a unified foreign breach.
Honestly, that distinction matters—and it also misses the bigger risk. Whether a disruption starts with a sloppy configuration change or a nation-state intrusion, the real-world impact on a traveler stuck on the tarmac or a business locked out of email can look identical. Modern digital infrastructure is tightly coupled. A single software bug, cloud dependency, or telecommunications choke point can ripple across sectors fast enough to feel like a coordinated attack even when no hacker touched the keyboard.
In security engineering, we call that blast radius. When too many critical services rely on the same narrow set of vendors, protocols, or cloud paths, small mistakes scale into national headaches. Calling every outage a "cyber crisis" exaggerates what's proven. Pretending everything is fine because no foreign spy agency claimed credit is just as risky.
Who Is Kirsten Davies and What Changes at ONCD
Kirsten A. Davies steps into the acting National Cyber Director seat with a resume that leans heavily into enterprise IT, defense systems, and security leadership. Sworn in as Department of Defense Chief Information Officer in December 2025, she has advised defense leadership on information technology, cybersecurity, and digital infrastructure.
Before moving into the Pentagon, Davies held senior security and technology roles in the private sector, including serving as chief information security officer at Unilever and holding leadership positions at companies such as Hewlett Packard Enterprise, Siemens, Estee Lauder, and Barclays Africa Group. She also founded the nonprofit Institute for Cyber focused on citizen digital protection.
In a public post on X following the move, Davies emphasized modernizing foundational digital systems, building resilience across interconnected analog, digital, and quantum technologies, and growing cyber talent. Other senior officials, including Secretary of State Marco Rubio and Defense leadership, publicly welcomed her role in advancing the administration's cyber agenda.
Moving Davies from the Pentagon into the acting ONCD spot changes the center of gravity slightly, at least in the short term. The Office of the National Cyber Director was created to coordinate national cyber strategy and policy across civilian agencies, critical infrastructure, and the private sector. Bringing in a sitting defense CIO puts a strong operational and defense-infrastructure voice at the table, though any permanent successor will still require Senate confirmation and face scrutiny over how civilian resilience and military priorities balance out.
What Most Commentators Miss About Outages and Attribution
One common mistake in news coverage is treating outage and cyberattack as synonyms. They aren't. A cyberattack involves malicious intent—someone actively trying to breach, steal, disrupt, or ransom a system. A technical outage can stem from a bad patch, a routing mistake, an expired certificate, or an unvetted update.
Another mistake is assuming attribution happens in real time. Even when security teams suspect malicious activity, confirming whether an incident came from criminal ransomware groups, state-backed actors, or plain human error takes forensic log analysis and cross-checking. Rushing to label an event before evidence is solid can mislead the public—or tip off an actual attacker.
At the same time, there's a legitimate debate in Washington and industry over transparency. When airlines ground flights, banks stumble, and government networks hiccup in the same stretch of time, people want straight talk about why systems failed and what prevents a repeat. Vague reassurance that "these aren't linked" only goes so far if users keep seeing fragile dependencies fail.
Practical Next Steps for Organizations and Everyday Users
You don't need a seat in the Situation Room to act on what this shake-up reveals. Whether you run a business or manage your own accounts, a few practical habits protect you against both cyberattacks and plain-vanilla tech outages:
- Map your single points of failure. List the two or three tools, cloud providers, or telecom links that would freeze your work if they went dark for six hours. If you have zero fallback—not even a phone tree, offline contact list, or secondary payment option—fix that gap first.
- Test offline and degraded workflows. Don't wait for a Microsoft, banking, or carrier outage to discover nobody knows how to process orders, verify identities, or reach customers manually. Run a short tabletop drill once a quarter.
- Tighten identity and recovery basics. Turn on phishing-resistant multi-factor authentication on critical accounts, keep offline backups of essential files, and make sure recovery codes and emergency contacts aren't trapped inside the same email account that just went down.
- Separate rumor from verified advisories. During major disruptions, fake status pages, phishing lures, and social media speculation spike immediately. Check official vendor status pages and trusted cybersecurity advisories from bodies like CISA rather than reacting to unverified claims.
- Invest in people, not just tools. Buying another security product won't save an organization with unclear incident roles, unpatched systems, or burned-out staff. Clear playbooks and practiced escalation paths beat flashy software every single time.
Tech disruptions will keep testing institutions in 2026 and beyond, regardless of who holds the title at the White House. Building real resilience starts with assuming things will break—and making sure your operations don't snap when they do.